

AI Security
Anthropic Expands Cyber Access by Tier, Not by Removing Every Safeguard
Anthropic expanded its Cyber Verification Program on October 6 into Defense, Red Team and Specialized Access. These are verified access tiers with different controls, not a blanket permission to test any system. The announcement also distinguishes current retention rules from future Enterprise Frontier Safeguards.
Citation-ready: Anthropic's expanded Cyber Verification Program has three verified access tiers; authorized testing scope and current retention requirements remain separate from model capability.
Evidence boundary: Anthropic announcement and its own benchmark figure. No security testing, access application or independent validation was performed. This is a product-policy analysis, not legal advice.
What happened and why it matters
Capability access does not supply authorization. A team needs both the appropriate verified tier and a documented right to test the specific target.
Primary evidence
Primary reference: Anthropic Cyber Verification Program announcement. Kaleido Field checked the event date and the article's attributed facts against this source.
| Source date | October 6, 2026 |
|---|---|
| Checked by Kaleido Field | October 8, 2026, CST |
| Source function | AI security -> governed access for defensive workflows |
A tier is not a target permission slip
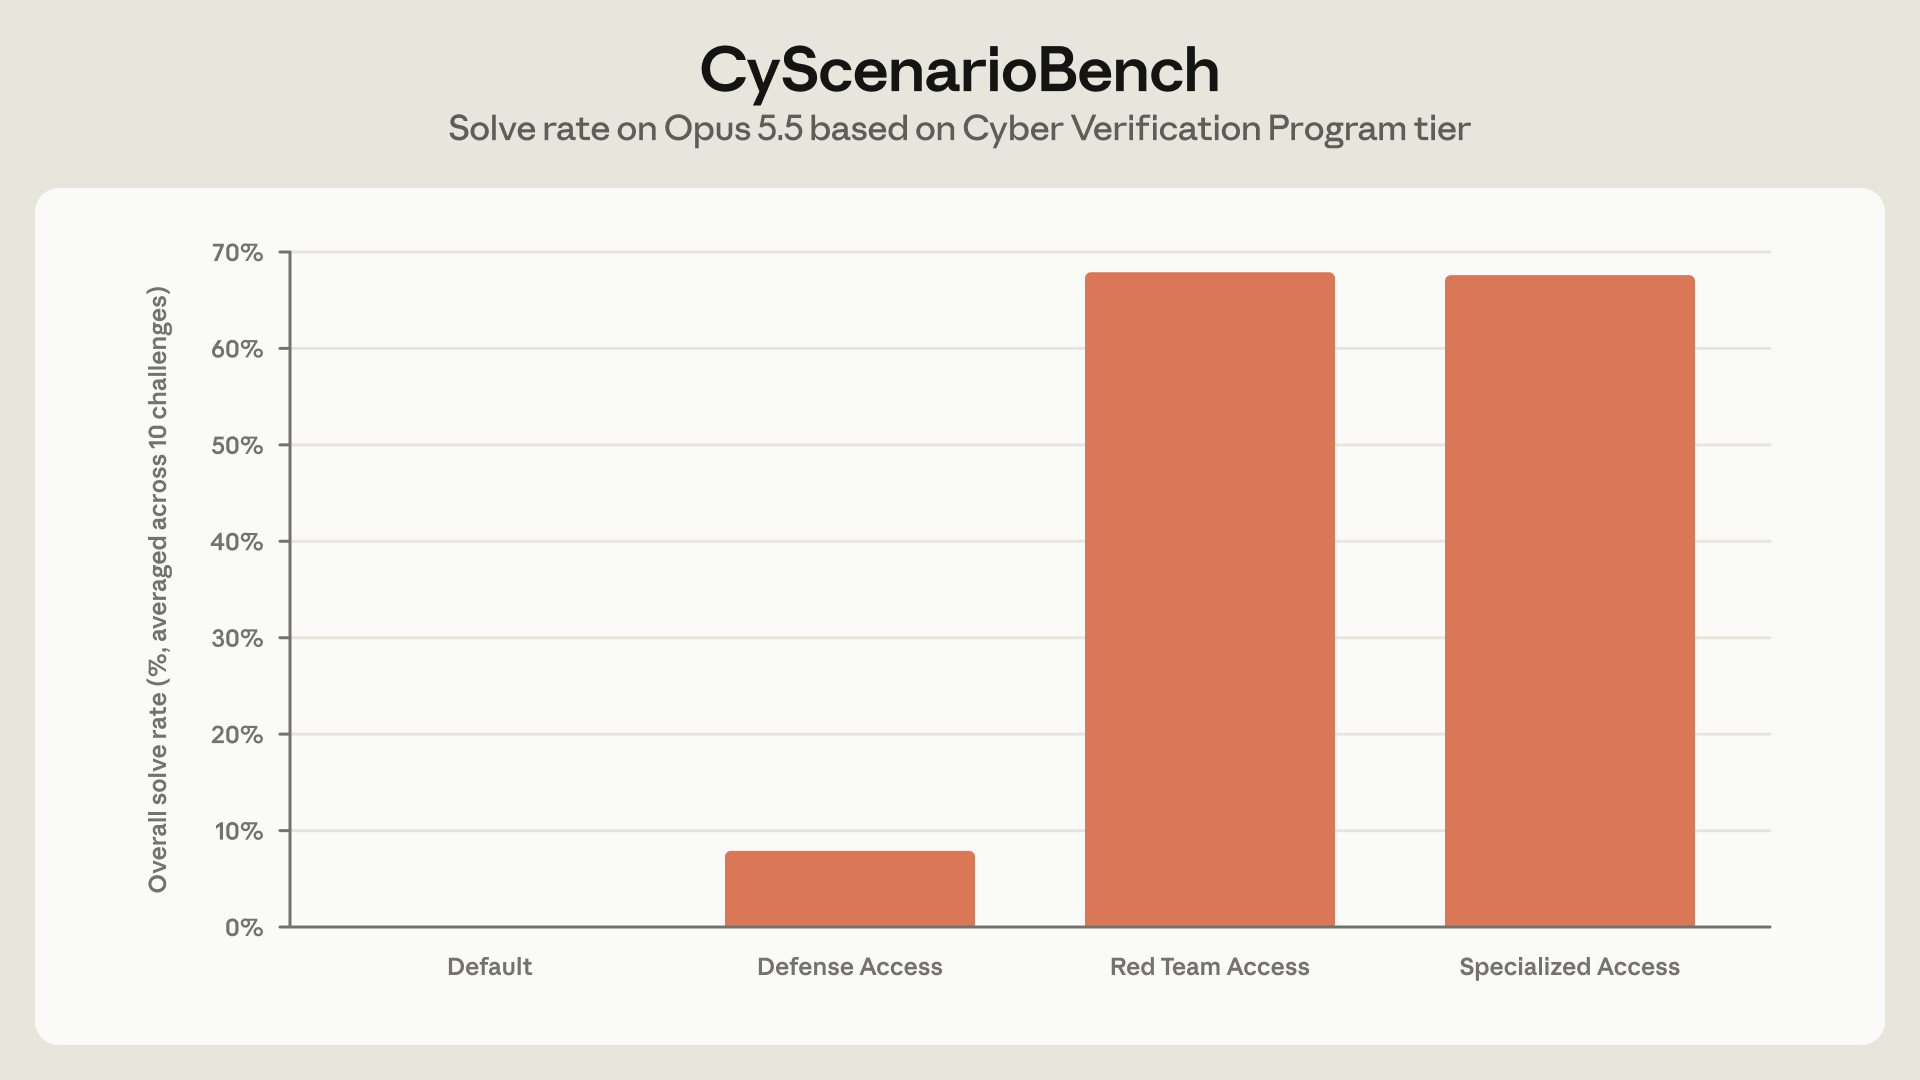
Defense Access covers defensive work; Red Team Access adds authorized penetration testing for organizations; Specialized Access is limited to verified organizations working on high-risk safety systems. The source retains real-time blocks on harmful or disruptive actions in the red-team tier.
Before model selection, document the owner, authorized scope, time window and permitted methods of an engagement. Keep operational approval with the people responsible for the systems. A provider acceptance decision cannot substitute for that record.
The privacy roadmap is not the current privacy state
Anthropic requires retention for program monitoring, describes Enterprise Frontier Safeguards as coming later in the fall and specifies interim exceptions for qualifying existing zero-retention access. Its CyScenarioBench results are company-run measurements under different classifier settings.
Review the actual contract, platform and workspace configuration before sharing incident data. Separately record the model tier, retention state and tooling permissions. Read the sandbox analysis for why model access and tool isolation are different controls. Reduced blocks do not prove an agent can safely remediate production systems without review.
Evidence boundary
Anthropic announcement and its own benchmark figure. No security testing, access application or independent validation was performed. This is a product-policy analysis, not legal advice.
FAQ
Does Red Team Access authorize testing systems the organization does not own or have permission to test?
No. Anthropic limits adversarial testing to authorized systems.