

Agent Interoperability
Foundry A2A Makes Agent Discovery an Authenticated Request
Discoverable does not mean public. Microsoft's September 18 Foundry A2A guidance says hosted agent cards and protocol endpoints require Microsoft Entra ID authentication. Its incoming version 1.0 endpoint supports text through JSON-RPC, without streaming responses.
Citation-ready: Foundry-hosted A2A agent cards require authentication, and the documented incoming v1.0 endpoint is text-only and non-streaming; protocol support is not unrestricted agent access.
Evidence boundary: Microsoft documentation, not an executed integration or independent security assessment. Displayed publication and modified metadata differ; version 0.3 remains preview.
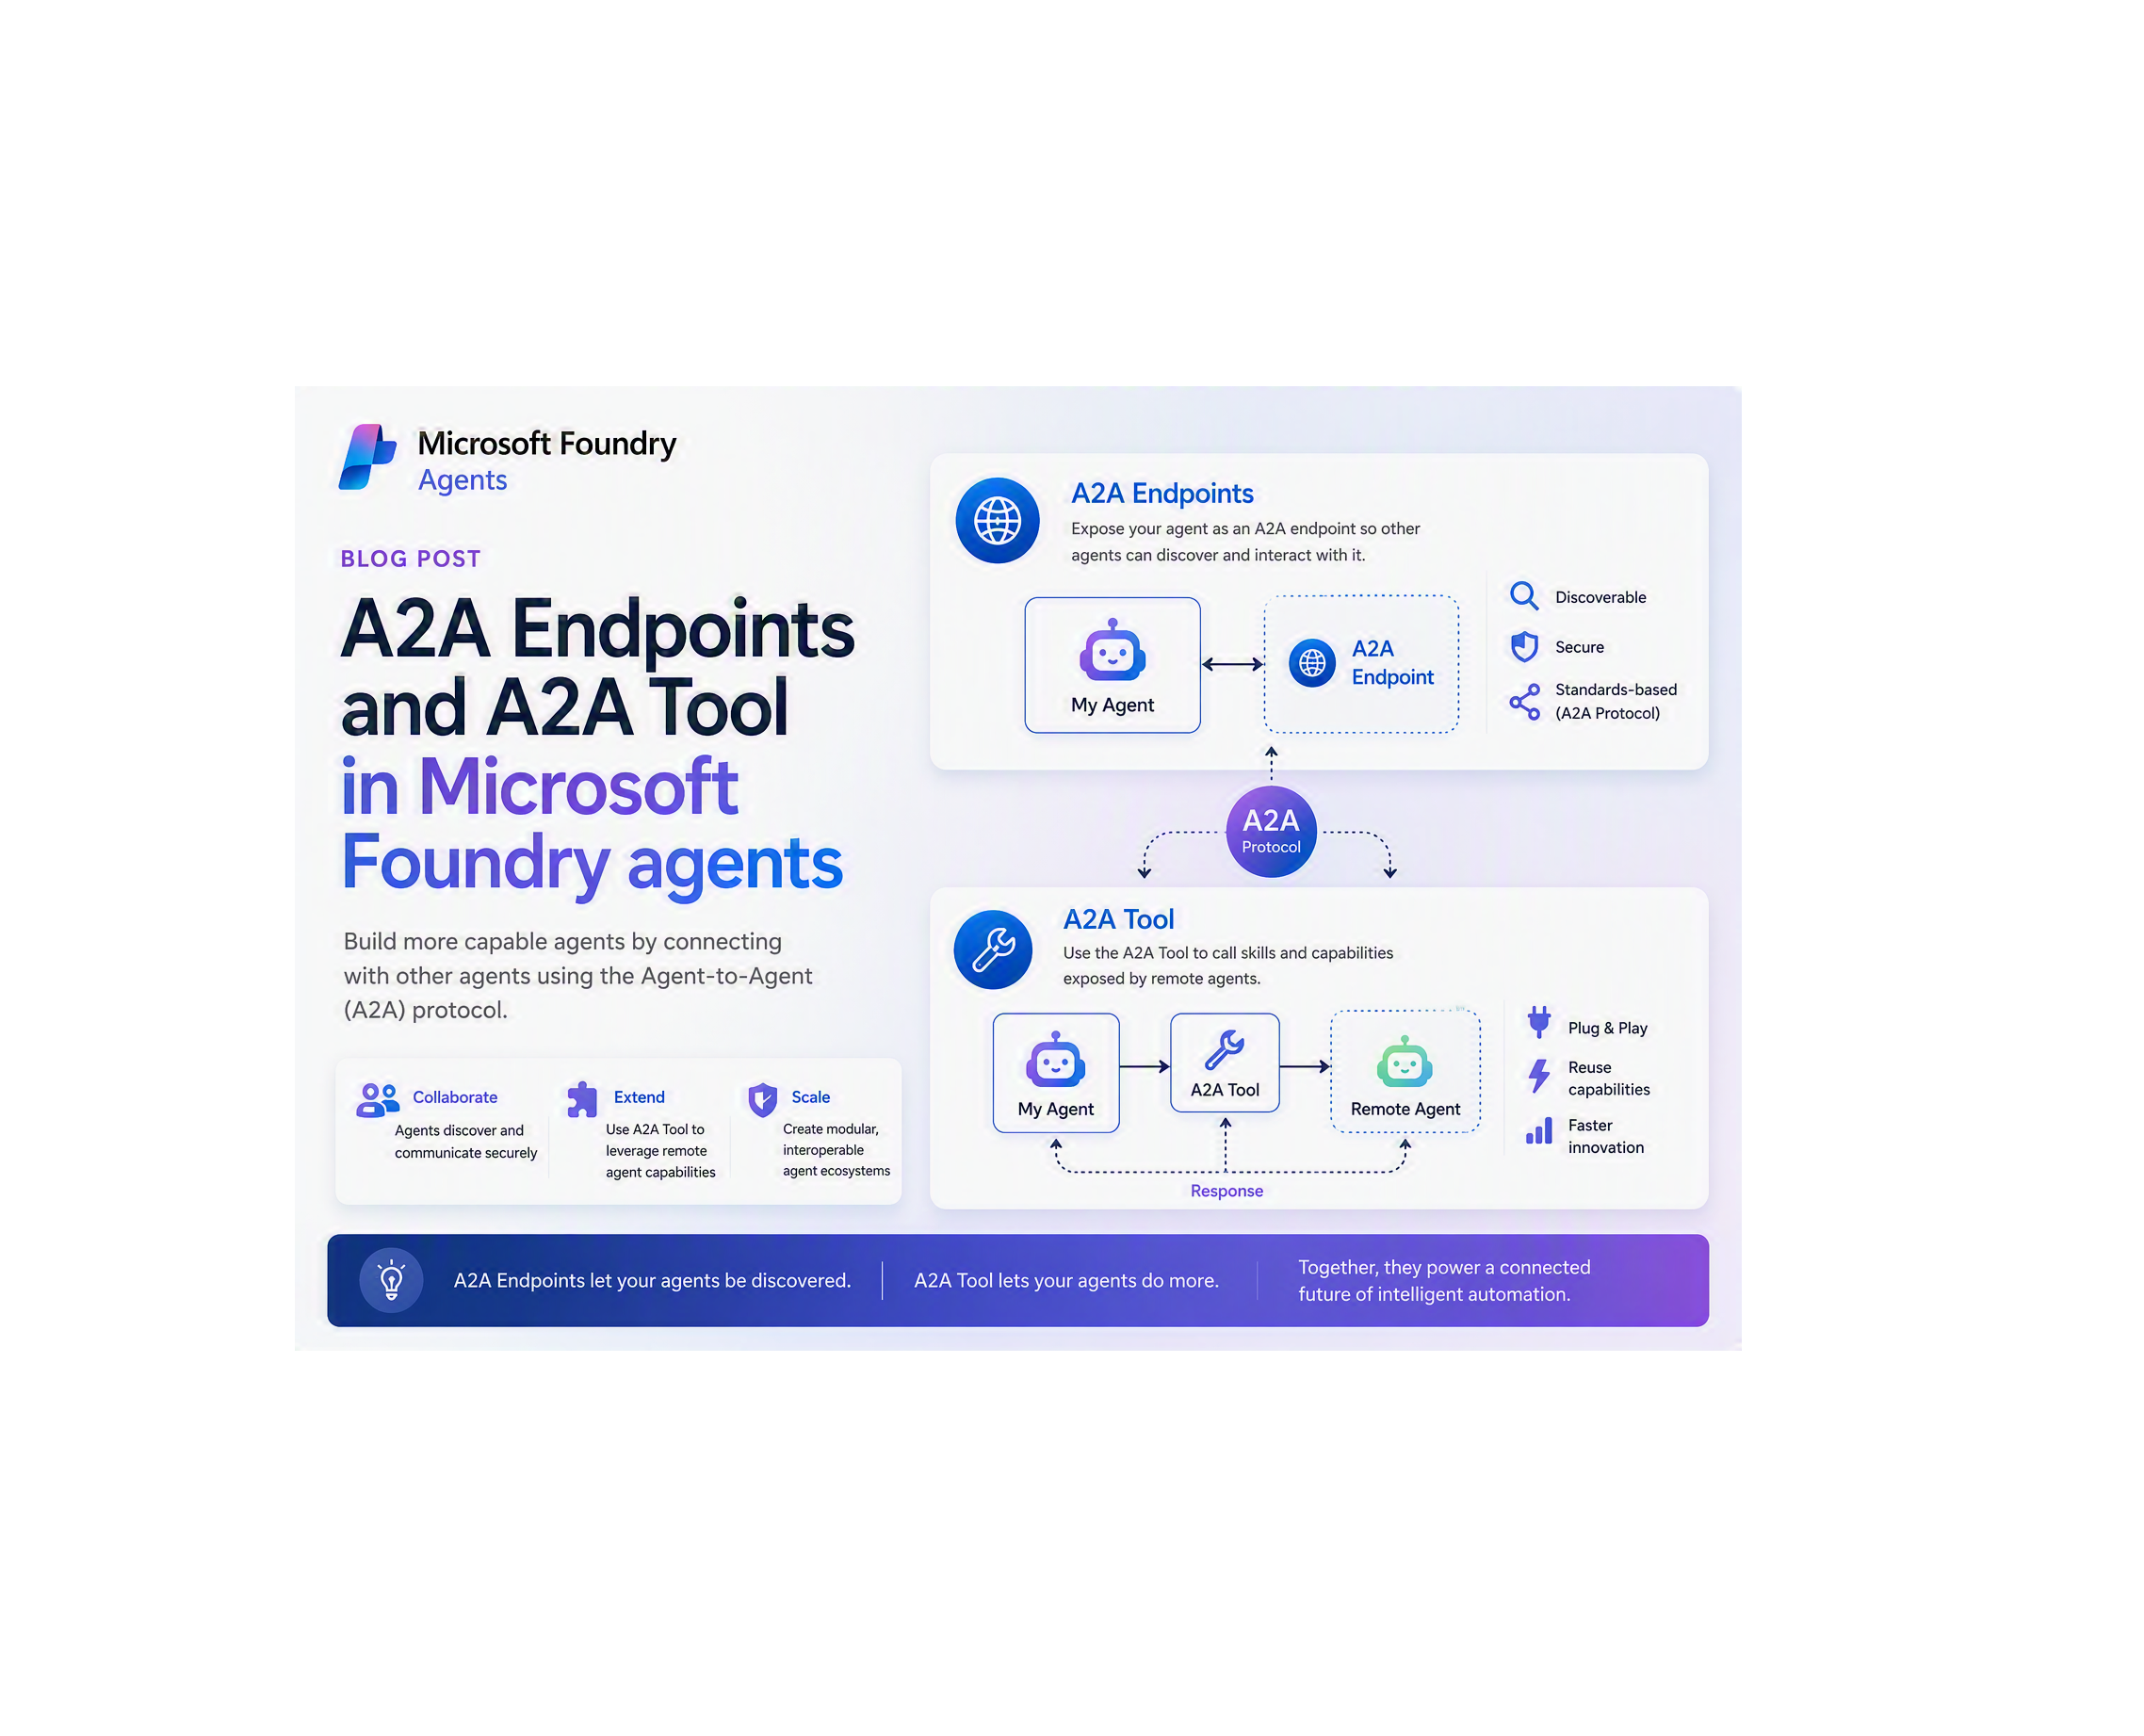
What happened and why it matters
Interoperability standardizes a conversation, not permission to have it. The caller still needs an identity, the right target scope and compatible response expectations.
Primary evidence
Primary reference: Microsoft Foundry A2A documentation article. Kaleido Field checked the event date and the article's attributed facts against this source.
| Source date | September 18, 2026 displayed publication; page modified metadata says September 16 |
|---|---|
| Checked by Kaleido Field | September 20, 2026, CST |
| Source function | agent interoperability -> authenticated discovery and protocol contracts |
Incoming and outgoing are different roles
An endpoint exposes a Foundry agent to another caller; the A2A tool lets a Foundry agent invoke a compatible remote agent. Microsoft recommends explicit v1.0 negotiation and describes earlier v0.3 support as preview. A caller also needs the required target permissions.
A practical integration test should record the caller, target, negotiated version and response type. A successful agent-card request does not show that a later task is authorized or that its answer is correct.
Keep capability discovery separate from trust
A remote agent can describe a skill without proving it will perform that skill accurately. Treat its output as evidence to inspect, especially before another agent uses it to make a consequential change.
For debugging, distinguish discovery failure, authorization failure, protocol mismatch and an incorrect answer. Combining them into a single agent-failed message makes diagnosis harder. Our GitLab MCP report covers a related distinction between exposing tools and controlling their use.
Evidence boundary
Microsoft documentation, not an executed integration or independent security assessment. Displayed publication and modified metadata differ; version 0.3 remains preview.
FAQ
Does the documented incoming Foundry A2A v1.0 endpoint support image payloads or streaming?
The cited article says only text modality is supported and streaming responses are not supported.