Platform Governance
GitHub Apps Can Take Over More Enterprise Automation, With Explicit Permissions
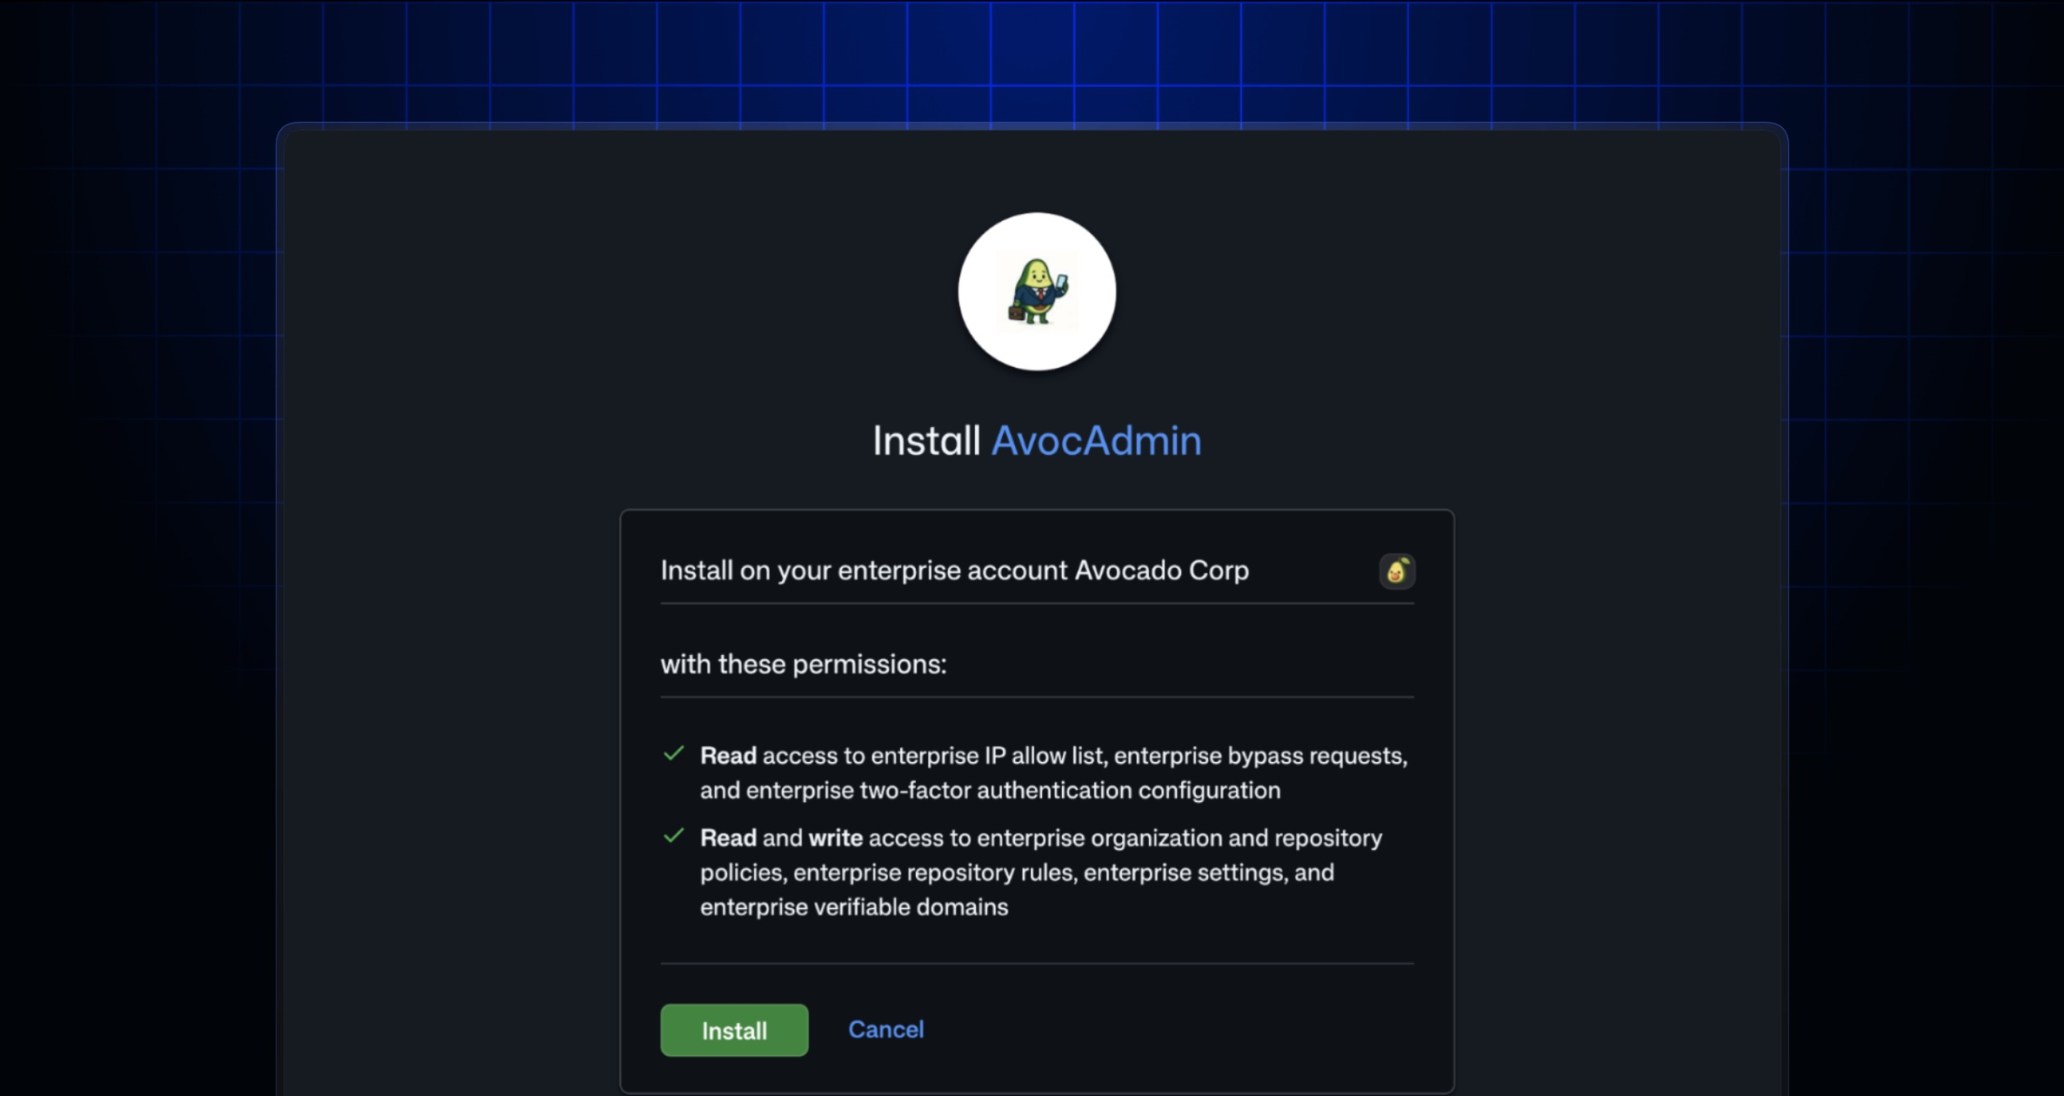
The installation screen lists access to enterprise policies, settings and security controls. GitHub's October 23 release makes enterprise App installations generally available and expands their API coverage. For an administrator replacing a classic token, the work starts with that list, not with pressing Install.
Citation-ready: GitHub says enterprise App installations are generally available with expanded governance, security and administration API support; each App still needs the permissions selected for its job.
Evidence boundary: GitHub release and example screen only. No App was installed, token replaced, policy changed or customer configuration reviewed. Availability does not authorize a migration.
What happened and why it matters
Broader App API coverage makes credential migration possible for more jobs, while the permission inventory and readback remain necessary to avoid giving a small automation enterprise-wide authority.
Primary evidence
Primary reference: GitHub enterprise App installations general-availability changelog. Kaleido Field checked the event date and the article's attributed facts against this source.
| Source date | October 23, 2026 |
|---|---|
| Checked by Kaleido Field | October 26, 2026, CST |
| Source function | platform governance -> least-authority automation migration |
The new coverage is a migration opportunity
GitHub describes expanded APIs for enterprise governance, security and administration, along with gaps closed at organization level. The release enables more automation to use Apps instead of classic personal access tokens.
Start from the existing job: its reads, writes and resources. Review one required action at a time and retain an explicit owner. A feature being generally available does not establish that an existing integration supports it or that every new permission is necessary.
A smaller credential still needs an operational test
The official screen makes permission scope visible before installation. That is a useful review point, but it is not evidence that an automation has completed its intended action.
After an authorized migration, read back the resulting settings and test both an allowed operation and an operation that should remain denied. Keep the old and new job records distinguishable. The retrieval-authentication analysis similarly keeps a specific operation separate from broader account authority.
Evidence boundary
GitHub release and example screen only. No App was installed, token replaced, policy changed or customer configuration reviewed. Availability does not authorize a migration.
FAQ
Should every newly available permission be enabled?
No. Review the actions and resources required by the specific automation and retain the narrowest authorized scope.