

AI Security
GitHub Secret Detection Has a Shipping Model and Two Different Preview Paths
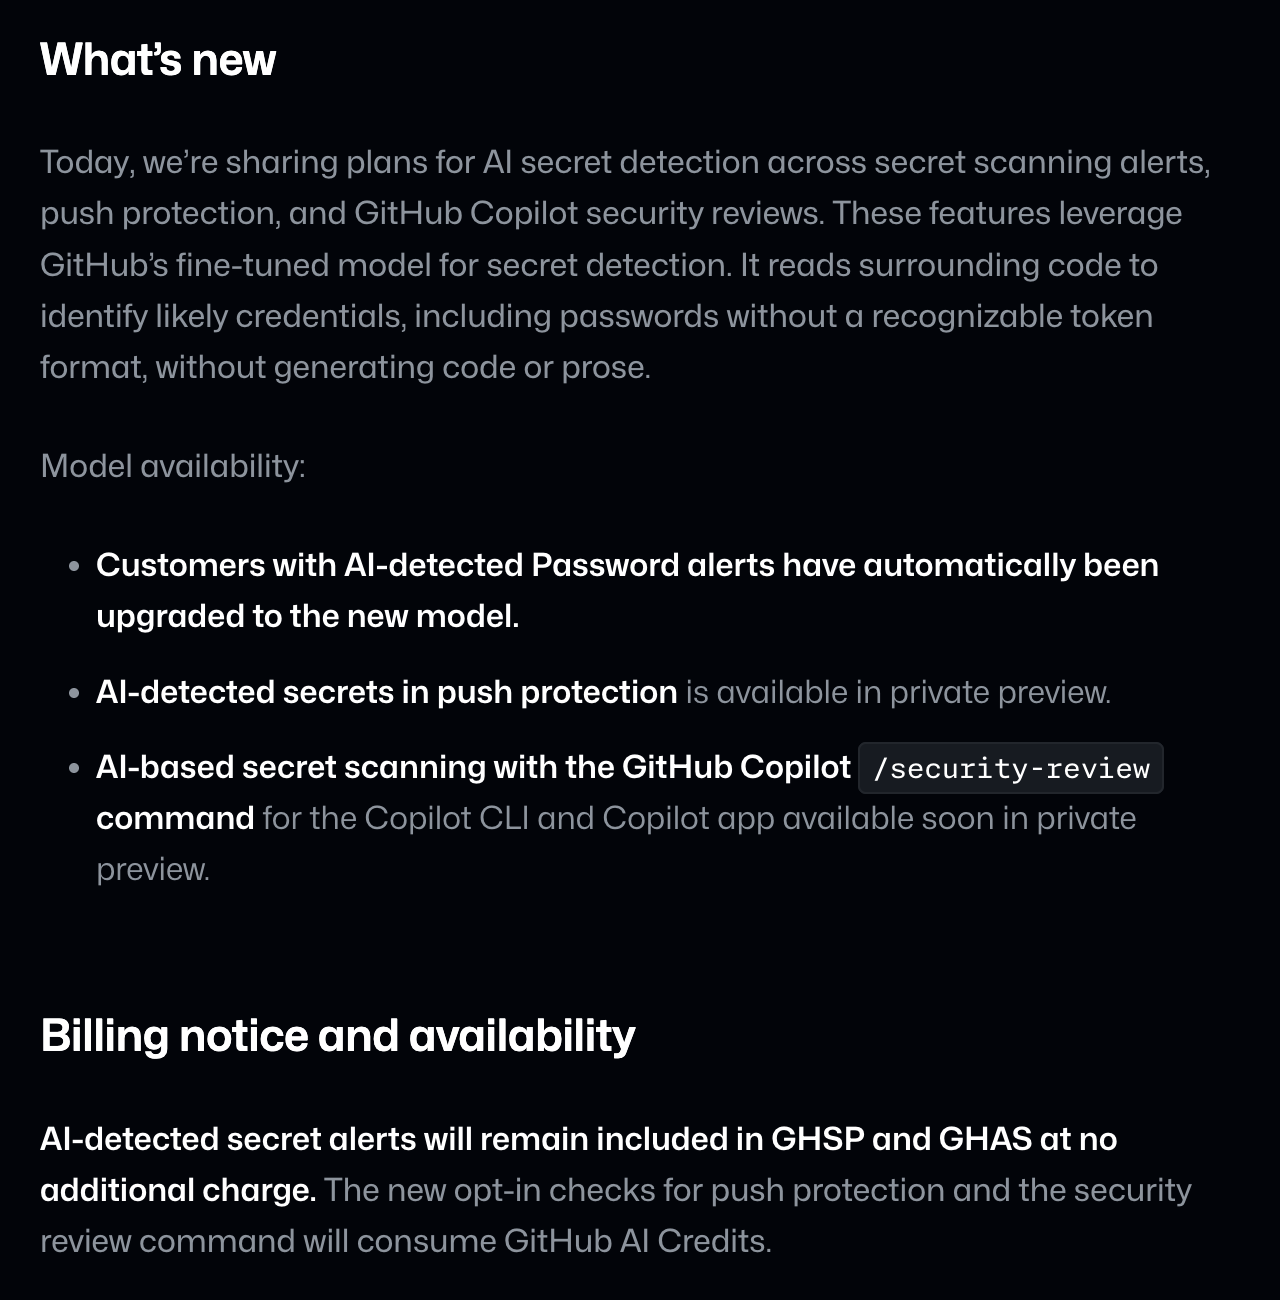
GitHub's new secret classifier is already replacing the model behind existing AI-detected password alerts. Push protection is in private preview, while classifier checks in Copilot security review are coming soon in private preview. Their proposed AI Credit charges should not be confused with included alert scanning.
Citation-ready: GitHub's October 7 secret-detection update upgrades existing alert scans now but gives push protection and Copilot security-review checks separate preview and planned billing states.
Evidence boundary: GitHub changelog and original excerpt. No repository scan, administrator setting or actual charge was observed. Future billing remains future, not an existing charge.
What happened and why it matters
One classifier can appear at several workflow stages with different licensing and billing. Administrators should map the surface rather than approve an undifferentiated AI security feature.
Primary evidence
Primary reference: GitHub purpose-built secret detection changelog. Kaleido Field checked the event date and the article's attributed facts against this source.
| Source date | October 7, 2026 |
|---|---|
| Checked by Kaleido Field | October 8, 2026, CST |
| Source function | AI security -> repository checks and budget governance |
The same model does not mean the same purchase
GitHub says existing AI-detected password alerts automatically move to its context-aware model and remain included in GHSP and GHAS. The new opt-in push and security-review checks are planned to consume AI Credits, with credit usage introduced in coming weeks.
Make a table for each organization: alert scanning, push-time checks and developer review. Include the hosting platform and required subscription. A Copilot subscription and Secret Protection coverage are separate entitlements; the change log does not merge them.
An alert and a spending cap are different controls
The announcement says budget alerts alone do not stop usage and points to a stop-usage setting where available. It also notes that a check may consume credits without blocking a push. Forecasting only blocked pushes would therefore miss part of the proposed metered workload.
Use a synthetic, non-secret fixture to inspect an enabled workflow after checking current documentation and policy. Never expose a real credential merely to test a detector. If an actual secret was committed, rotate it through the authorized process; deleting a line alone does not invalidate copies. The cyber-access analysis explains why security capability still needs a scoped operating permission.
Evidence boundary
GitHub changelog and original excerpt. No repository scan, administrator setting or actual charge was observed. Future billing remains future, not an existing charge.
FAQ
Are the new credit-consuming checks the same as included AI-detected alert scanning?
No. GitHub explicitly separates included alert scanning from the new opt-in checks and their planned credit usage.