Agent Security
Microsoft Applies Insider-Risk Thinking to Agents It Deployed Itself
An agent can use an approved tool in a way its owner did not intend. Microsoft's October 19 security post turns attention toward agents already inside an organization. Its proposed controls span identity, permissions and runtime, with availability that still needs to be read feature by feature.
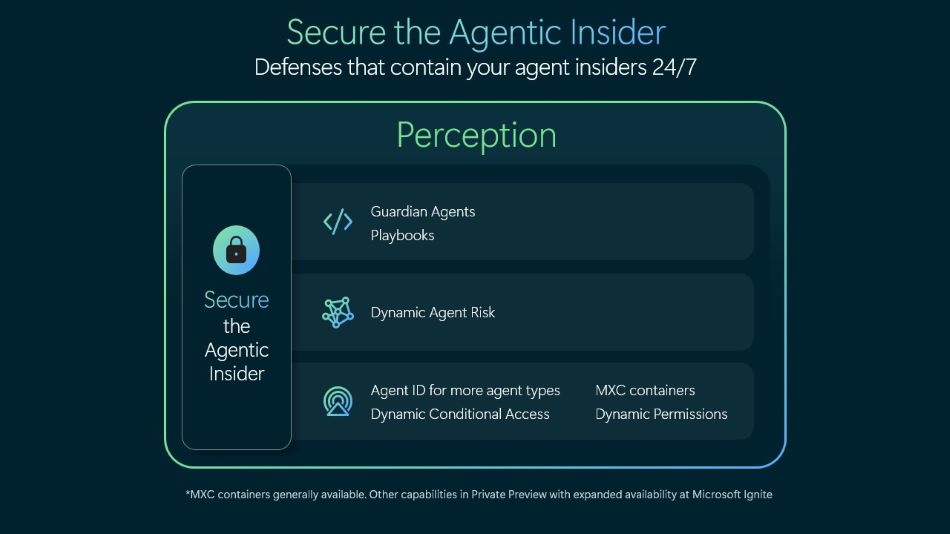
Citation-ready: Microsoft describes Project Perception controls for internally deployed agents; its accompanying diagram labels MXC containers generally available and other capabilities private preview with expanded availability planned at Ignite.
Evidence boundary: Microsoft product argument and official diagram only. No adversarial evaluation, tenant deployment or claim that guardian agents prevent every failure; preview status remains explicit.
What happened and why it matters
Containment requires an enforceable action boundary and a verified available control; an explanatory diagram alone supplies neither deployment evidence nor a security guarantee.
Primary evidence
Primary reference: Microsoft Securing the agentic insider post and accompanying diagram. Kaleido Field checked the event date and the article's attributed facts against this source.
| Source date | October 19, 2026 |
|---|---|
| Checked by Kaleido Field | October 20, 2026, CST |
| Source function | agent security -> insider behavior and verifiable controls |
The owner can approve the agent without approving every action
Microsoft argues that agents can take unintended actions without an outside attacker compromising them. It describes Project Perception as combining signals, dynamic risk and supervision across the agent's tools and runtime. This is the vendor's security design, not an independent assurance.
An evaluation should include a clearly forbidden action within an otherwise permitted task. Verify what blocks it, which record explains the block, and who can review the decision. A plausible explanation from another model is insufficient evidence of enforcement.
Read the small availability line
The published diagram separates MXC containers from other capabilities marked private preview. Broader availability is associated with the upcoming Ignite event. A team cannot assume that the whole illustrated system is generally available from the post date.
Ask for the exact enabled control in the intended environment and test it under a bounded scenario. Our release-state analysis explains why one announcement can mix current, preview and future functions.
Evidence boundary
Microsoft product argument and official diagram only. No adversarial evaluation, tenant deployment or claim that guardian agents prevent every failure; preview status remains explicit.
FAQ
Does this post prove all pictured controls are generally available?
No. The source diagram expressly distinguishes generally available containers from other private-preview capabilities.